Req 2.90: The Supplier shall maintain independent third-part...
📋 Requirement Details
Req 2.90: The Supplier shall maintain independent third-party security testing, including penetration tests or vulnerability assessments conducted within the last twelve (12) months. Such test results or attestations shall be made available to DepEd upon request, subject to non-disclosure constraints.
⚙️ Technical Demonstration
IMTLazarus completely satisfies this requirement by leveraging a multi-layered security testing framework that combines continuous software-layer vulnerability management with annual independent third-party audits of our underlying edge and hosting infrastructure (partnered with Zenlayer). This ensures that the entire operating environment undergoes rigorous security validation within the mandated twelve (12) month cycle:
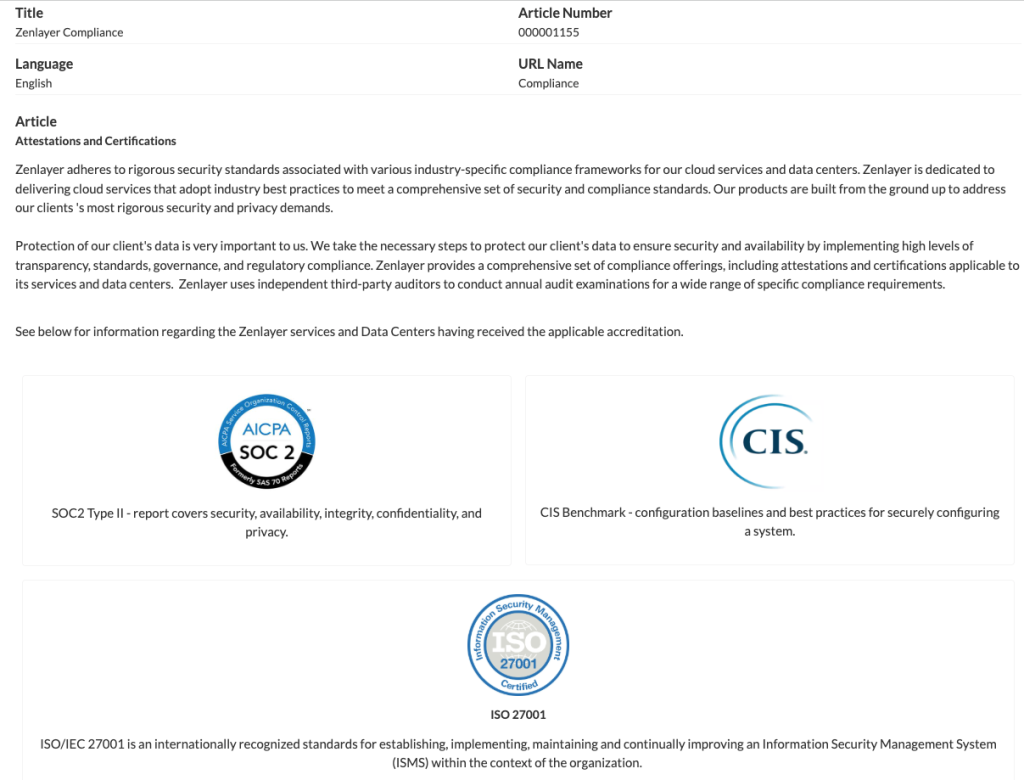
- Annual Third-Party Infrastructure Audits: The platform's global cloud services and hosting data centers are subjected to regular annual examinations conducted by independent, accredited third-party auditors. These examinations validate compliance with rigorous security frameworks, including SOC 2 Type II standards (covering security, availability, integrity, confidentiality, and privacy) and ISO/IEC 27001 Information Security Management Systems (ISMS).
- Hardened Configuration Baselines: To prevent infrastructure vulnerability, system components are configured and audited against CIS Benchmarks. This ensures that the operating systems, cloud containers, and network elements delivering the IMTLazarus solution to DepEd follow established industry best practices for secure configuration.
- Controlled Access to Attestations: In strict compliance with the requirement, the formal compliance certificates, audit summaries, and third-party validation attestations generated within the last twelve (12) months will be made available to authorized DepEd ICT leadership upon request, subject to standard mutually agreed non-disclosure and confidentiality constraints.
Security Assessment and Audit Framework
The testing and audit methodology covers both the physical hosting architecture and the logical systems configuration:
| Evaluation Type | Testing Body & Framework | Assessment Scope | Availability to DepEd |
| Infrastructure Audit | Independent Third-Party Auditors (SOC 2 Type II / ISO 27001) | Physical data center security, data encryption redundancy, operational availability, and confidentiality controls. | Available upon demand under standard Non-Disclosure Agreement (NDA). |
| System Hardening Verification | CIS Benchmarks Auditing Standards | Validation of secure, baseline configurations across hosting components to prevent system-level vulnerabilities. | Available upon demand under standard Non-Disclosure Agreement (NDA). |
| Application Security | Routine Vulnerability Reviews | Validation of software-layer integrity and administrative dashboard defense frameworks. | Provided as executive compliance summaries during formal turnover. |
🖼️ Visual Evidence