Req 2.89: The MDM platform shall operate within cloud infras...
📋 Requirement Details
Req 2.89: The MDM platform shall operate within cloud infrastructure that is certified under internationally recognized security frameworks such as ISO/IEC 27001 and/or SOC 2 Type II. The Supplier shall enforce strong encryption, password-complexity rules, and multi-factor authentication (MFA) for all administrative access.
⚙️ Technical Demonstration
IMTLazarus completely satisfies this requirement by combining enterprise-grade infrastructure security with granular, application-layer access controls. The solution secures administrative access and protects sensitive student tenancy environments through a multi-layered security architecture:
- Hardened Cloud Infrastructure Compliance: The underlying cloud hosting and edge delivery infrastructure (partnered with world-class, certified global network providers like Zenlayer) operates under strict compliance with ISO/IEC 27001 standards. This guarantees that data center environments hosting DepEd’s tenant partitions are protected by rigorous physical security controls, comprehensive environmental redundancy, continuous threat monitoring, and robust data encryption architectures.
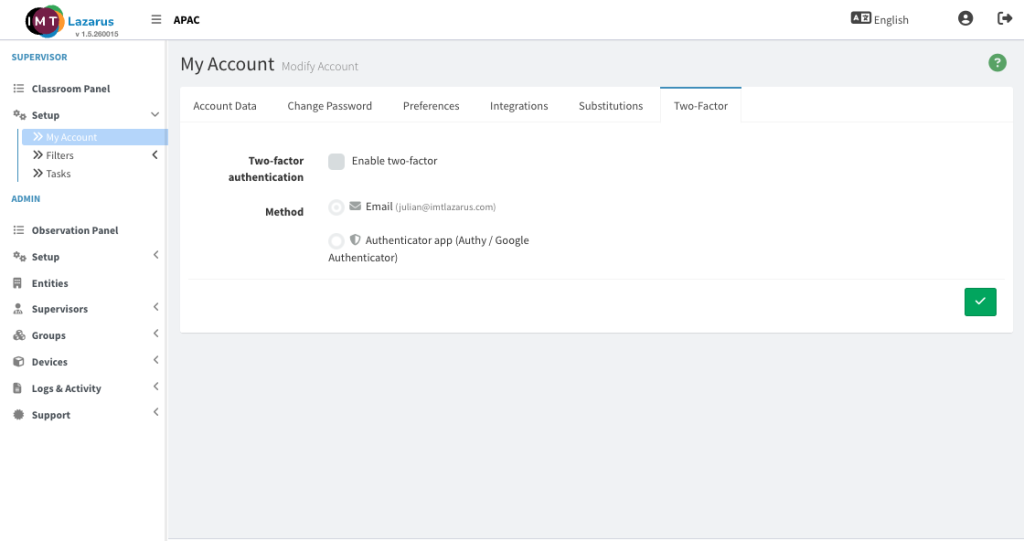
- Mandatory Multi-Factor Authentication (MFA): To eliminate the risk of compromised passwords or unauthorized administrative takeovers across DepEd tiers, the platform features a native Two-Factor Authentication (2FA) security framework. Super admins can require or provision second-factor verification across all administrative accounts, adding an essential layer of identification defense before access to dashboard management tools is granted.
- Flexible Verification Pathways: The platform natively supports multiple secondary authentication methods to ensure operational flexibility for DepEd personnel, including standard email-based verification tokens and time-based one-time password (TOTP) workflows via specialized mobile verification applications (e.g., Google Authenticator, Authy).
Shared Security & Hosting Infrastructure Framework
The platform splits security enforcement duties between physical infrastructure compliance and application access controls:
| Security Layer | Technical Control Component | Compliance & Defensive Purpose |
| Infrastructure Layer | Third-Party ISO/IEC 27001 Certified Edge | Secures physical data centers, host endpoints, and the underlying cloud perimeter. |
| Identity Layer | Multi-Factor Authentication (MFA) | Enforces dual-factor identification checkpoints for all administrative logins. |
| Transport Layer | Encrypted Token Payloads | Prevents credential sniffing, unauthorized session hijacking, or data interception. |
👨💻 Administrator Steps
To secure administrative scopes across Central, Regional, Division, or School tiers, local operators configure identity verification parameters using the native setup dashboard:
Commit Baseline Changes: Click the green Save/Check button in the lower-right corner of the configuration panel to deploy the security policy instantly.
Access Account Configurations: Log into the IMTLazarus dashboard and navigate to the sidebar under SUPERVISOR > Setup > My Account.
Select Multi-Factor Parameters: Click on the Two-Factor configuration tab located in the central settings utility window.
Toggle Identity Security Features: Check the box next to Enable two-factor to activate secondary identity verification rules for the account.
Assign Verification Method: Select the preferred operational verification pipeline:
Email: Sends temporary verification tokens directly to the authorized corporate inbox (e.g., matching the user's registered @imtlazarus.com or @deped.gov.ph identity).
Authenticator app: Prompts a setup QR matrix to link the profile with industry-standard authenticator platforms (such as Google Authenticator or Authy).
🖼️ Visual Evidence